# 5 Free Tools to Find SQL Injection and XSS Before Hackers Do
A hacker once told me the easiest way into most web apps is the login form.
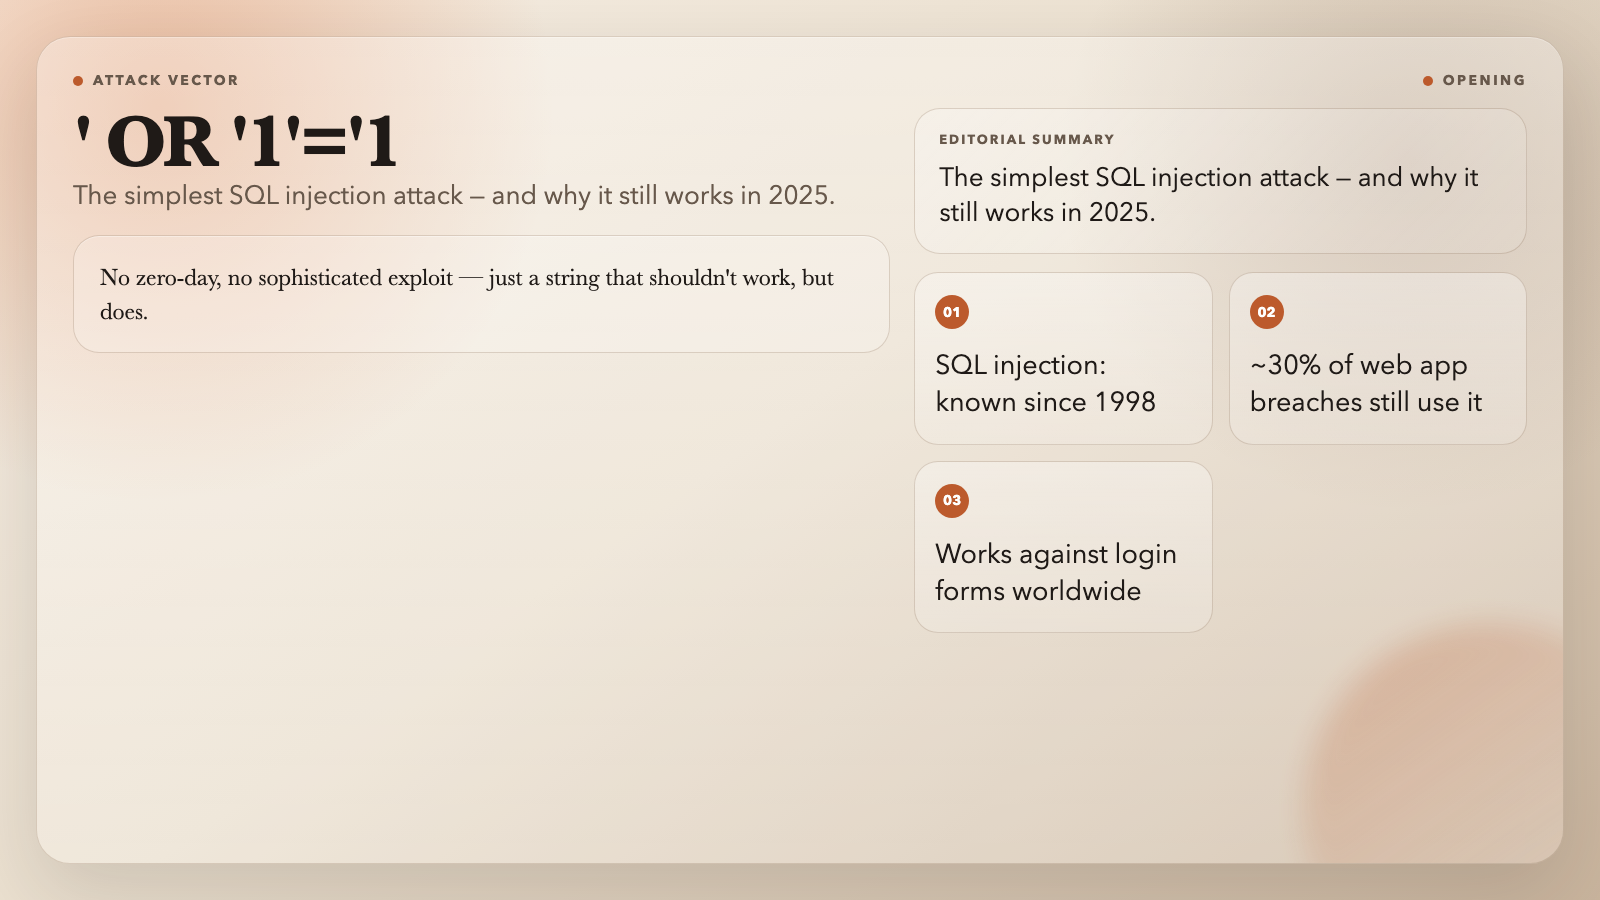
You type `’ OR ‘1’=’1` in the username field, hit Enter, and you’re in. No zero-day, no sophisticated exploit — just a string that shouldn’t work, but does. SQL injection has been a known vulnerability since 1998. It still shows up in breach reports in 2025, behind roughly 30% of web application attacks.
The same goes for cross-site scripting (XSS). It doesn’t need a sophisticated attack chain. Drop a `
Posted in未分类
5 Free Tools to Find SQL Injection and XSS Before Hackers Do
Posted by
 By
No Comments
 By
No Comments