8 Free Developer Tools That’ll Save You Hours of Tedious Work
You’ve been waiting on a backend team for two weeks. Your PM wants a demo Friday. Instead of waiting — you build the mock yourself in 30 seconds and ship the feature.
That’s the thread running through every tool here: tasks that burn hours, but don’t have to.
1. API Mock Server — Test Your Frontend Before the Backend Exists
The API Mock Server takes a JSON description of your endpoints and spins up a working mock server backed by Redis. It lives for one hour, gets a unique ID, and accepts hot updates — run the same ID again and the responses refresh instantly without restarting anything.
You can template dynamic values directly into responses: {{params.id}}, {{body.username}}, {{now}}. Instead of maintaining a static mock data file for every edge case, you define the shape once and the mock fills in the blanks at runtime.
The scenario that lands: building a user profile page. Define GET /users/:id and POST /login, and your frontend is testing real UI against real response structures before a single backend line ships.
2. JSON Schema Validator — Know Your Data Is Actually Valid
When two services break at integration, the first question is always “is the data what we think it is?” Hand-comparing JSON is miserable. JSON Schema Validator does it in seconds.
Paste your JSON and a JSON Schema, pick a draft version (Draft 4 through 2020-12), and it reports exactly what’s wrong and where — path, error type, and the specific failure. It uses AJV under the hood and runs entirely in the browser. No server. No signup.
Schema mismatches between producer and consumer services silently break production. Catching them at the schema level costs minutes. Debugging the same mismatch in production costs hours.
3. Regex Tester — Stop Guessing, Start Matching
Regular expressions are concise and nearly unreadable. When something breaks, you open a tab, paste the pattern, and start guessing which flag is wrong.
The Regex Tester removes the guesswork. Enter your pattern, pick your flags (g, i, m — whatever you need), paste your test text, and it shows every match with position. No reloads. No console. It handles the edge cases that trip people up constantly — multiline matching, case sensitivity, global vs. first-match behavior, all visible in one view.
4. Code Complexity Analyzer — Before You Add That Feature, Read This First
You open a function. It’s 200 lines. Three nested ternary operators. You add the feature. Six months later, nobody can touch it without introducing bugs.
The Code Complexity Analyzer gives you an honest picture of what you’re about to inherit. Drop in JavaScript, TypeScript, Python, Java, or Go — it auto-detects the language — and it measures cyclomatic complexity, cognitive complexity, nesting depth, and duplicate code windows across your entire file.
Unlike a basic linter, it distinguishes between cyclomatic complexity and cognitive complexity. A function can have low cyclomatic complexity but high cognitive complexity because of deeply nested state. That distinction tells you what to refactor first. It also flags duplicate code windows and tells you exactly which lines they’re on.
5. API Request Code Snippet Generator — Stop Rewriting the Same Request in Six Languages
You have a working request in your browser devtools. Now you need it as a cURL command in Slack, as a Python script for the data team, and as a usage example in the README. Three formats for the same request.
The API Request Code Snippet Generator handles this in one shot. Enter URL, method, headers, query params, and body. Pick your body type (JSON, form-urlencoded, plain text). It generates ready-to-use code for cURL, Fetch, Axios, Node.js fetch, Python requests, Go net/http, and PHP cURL — all with a copy button on each.
Practical use case: onboarding documentation. Paste actual working code examples in every language your team uses, instead of writing “see the API docs” and leaving it there.
6. OpenAPI to TypeScript Generator — Your API Types, Generated Automatically
Most TypeScript projects consuming REST APIs have the same problem: API types are hand-written and perpetually stale, or missing entirely. Every time the backend changes, someone manually updates the types — and gets something wrong.
The OpenAPI to TypeScript Generator takes an OpenAPI or Swagger spec (JSON or YAML) and generates TypeScript interfaces for every schema and endpoint. Output flat exports or a namespace wrapper. Pick PascalCase or camelCase. Choose interface or type alias. Include operation types and descriptions with a single checkbox.
Paste in your user service spec and you get User, GetUserPath, GetUserResponse — typed and importable in seconds. No more any types hiding in your API layer.
7. SQL Injection Detector — Find the Patterns Before Someone Else Does
You’re reviewing a pull request. Someone wrote a raw SQL query with string interpolation. You say “please use parameterized queries.” They say “it works for our use case.”
The SQL Injection Detector gives you evidence. Paste in the code, run a quick scan, and it flags patterns like ' OR '1'='1, UNION SELECT, '; DROP TABLE, WAITFOR DELAY, and 30+ other injection signatures. Quick scan catches obvious patterns. Full scan goes deeper.
The point isn’t that every flagged pattern is exploitable. The point is that string-interpolated SQL with user input is the class of vulnerability that has sat at the top of OWASP’s list for over a decade. A scanner won’t catch everything. It catches the patterns that indicate the problem exists.
8. XSS Payload Detector — Catch Cross-Site Scripting Before It Ships
XSS keeps appearing in breach reports. The problem isn’t that developers don’t know it’s dangerous — it’s that XSS payloads come in so many forms that code review misses most of them.
The XSS Payload Detector scans text or code for over 80 attack patterns across 10 categories: script tags, event handlers (onerror, onload, onclick, and 60+ others), JavaScript protocols, iframe/frame tags, SVG payloads, DOM manipulation patterns (innerHTML, eval, document.write), CSS expression injection, and URL/HTML entity encoded variants.
It reports risk level — LOW, MEDIUM, HIGH, or CRITICAL — for each finding and decodes obfuscated payloads before scanning. A %3Cscript%3E that decodes to gets caught. So does <script> and onerror hiding inside a Unicode-obfuscated attribute.
The Gap These Tools Don’t Fill
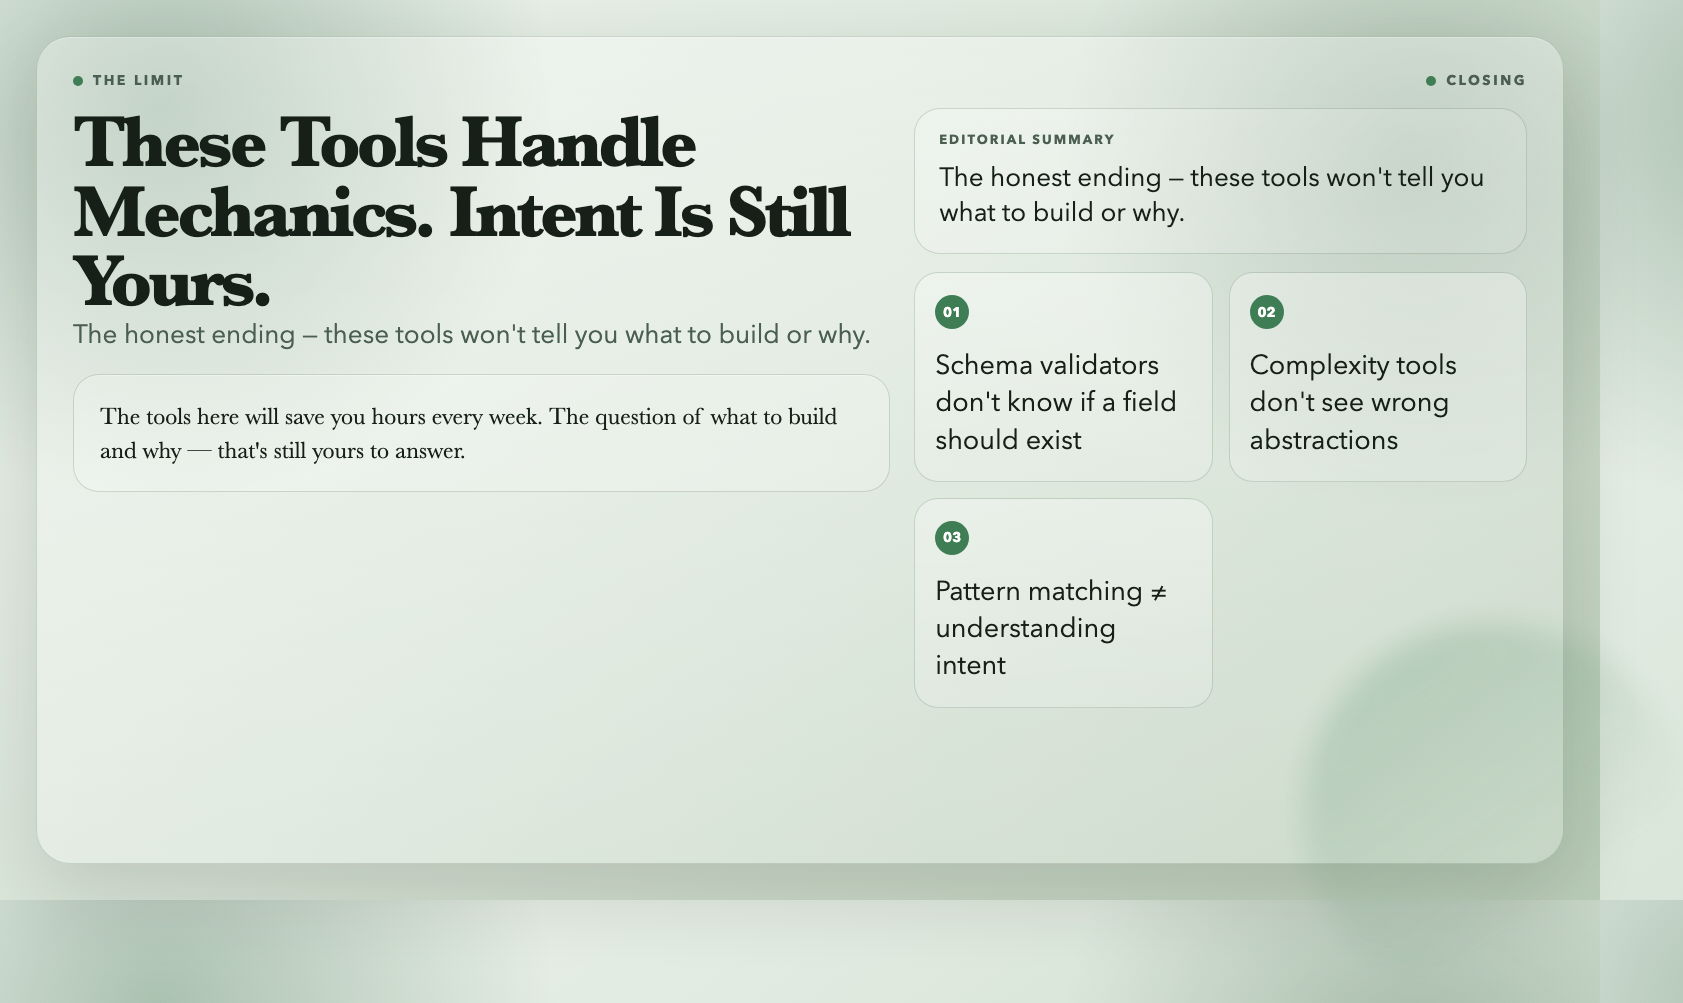
These tools handle the mechanical parts: catching patterns, generating boilerplate, validating shapes. They don’t understand intent.
A schema validator confirms your JSON is correct. It doesn’t tell you whether the field should exist. A complexity analyzer reports a tangled function. It doesn’t tell you whether the tangle is a symptom of a wrong abstraction upstream.
The tools here will save you hours every week. The question of what to build and why — that’s still yours to answer.